root@hamcodes: authorized use only

No fluff. No theory. Just execution.

how_to_hack_all_tech --practical --now

A field guide for operators who would rather run the command than read another chapter about it. Real tools, real syntax, real playbooks. Then two free courses you can start in this tab.
Red, blue and purple 2 free courses No sign-up
The Hacker's Notes, the book
night_shift --3d --interactive

Night Shift at Veltrix

A 3D security simulation you actually operate. Cover the late shift in accounts payable at a freight company: a real desktop of twenty apps, a mobile and a desk phone, and the attacks that really breach companies. No install, no sign-up, and nothing you do leaves your browser.
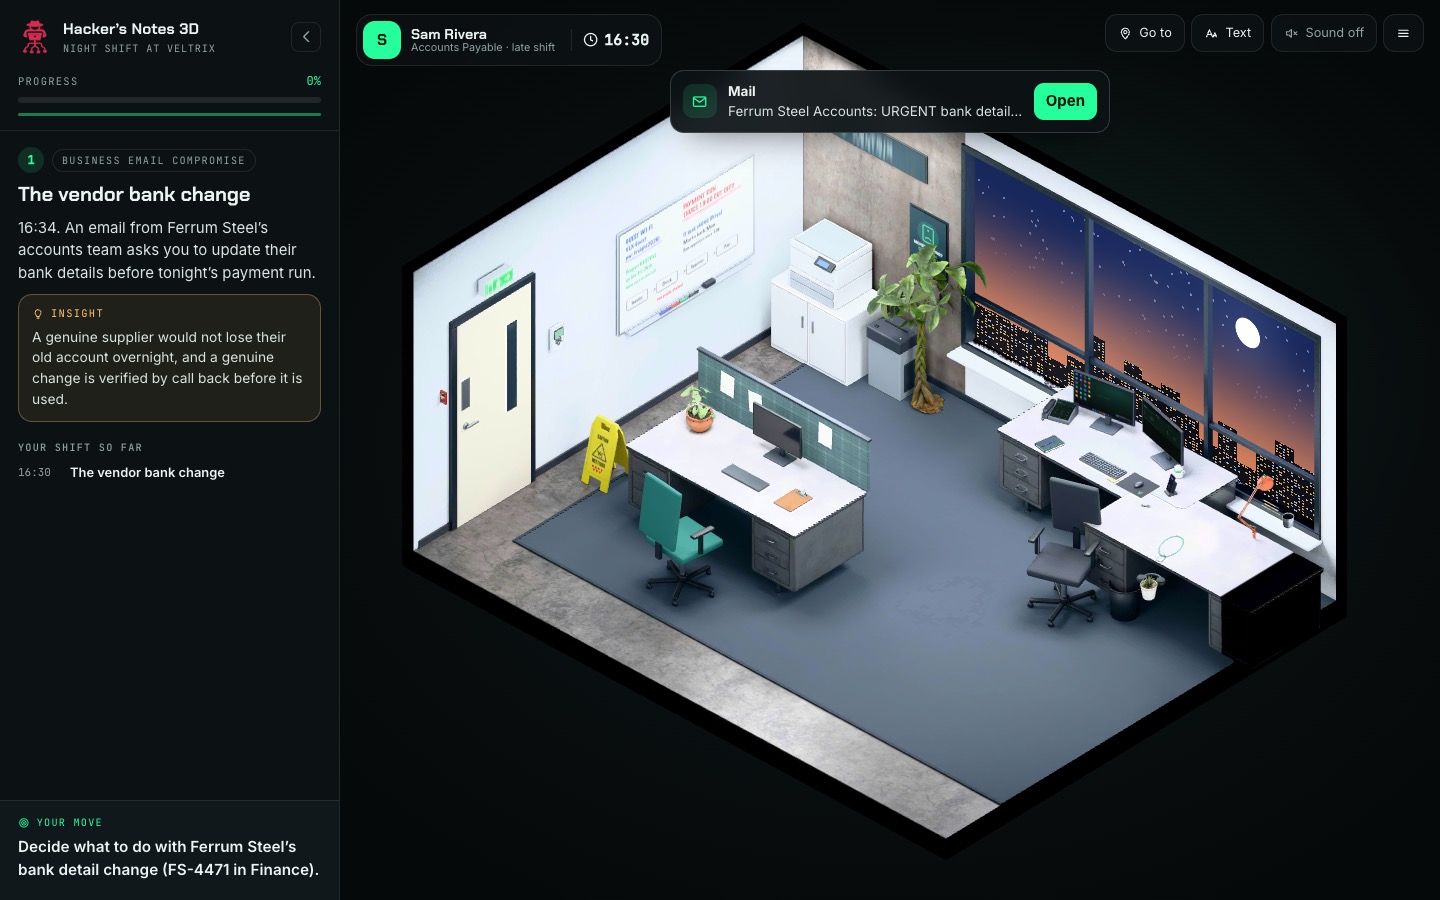
01Business email compromiseA supplier asks to change their bank details before the payment run closes.
02MFA fatigue & vishingYour phone floods with sign-in prompts, then a voice claiming to be IT calls.
03Prompt injectionA vendor PDF quietly tells your AI assistant to forward the finance mailbox.
veltrix_logistics: accounts payable, late shift
A freight company's finance office at night, rendered in 3D Live 3D exercise Tap to see how it works

Best on a laptop. Eight scenarios, six per shift, seeded so every run is different. A real computer and a real phone, not buttons on a video.

Open the full sim
hackers_python

Learn Python by building security tools

Real Python, in your browser, right now. No install and no sign-up. Four sections, 32 lessons, and a finished tool you keep at the end of each one.

01Password checkerScore a credential on length and character classes.
02Login detectorParse an auth log and flag brute-force attempts.
03Credential triageRate a whole dump and print a report.
section_01: fundamentals through a security lens

Section 1 is playable above. Progress saves by itself and carries over.

Play all 4 sections
free_course

Hack your cyber career

Ten modules, free, no sign-up. A career roadmap with the diagrams and over 180 checked links behind it: free training, free certifications, labs, books and job boards. Pick a lane, build proof instead of a wish list, and handle the interview.

Free to read, nothing to install, no email required.

Start the free course
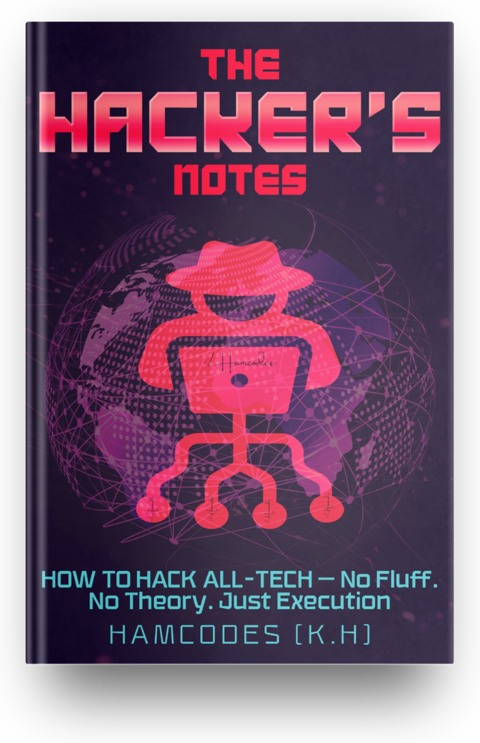
The Hacker's Notes cover
the_field_guide

How to Hack All-Tech

The book the rest of this site came out of

A streamlined, field-tested guide focused on what you actually do. Every chapter ships command-line syntax and real tool usage, updated for 2025 systems and toolchains.

  • Direct execution. Skip the theory, start at the hands-on step.
  • Toolkits that run. Scripts, commands and playbooks for red and blue.
  • Modern coverage. AI and ML, blockchain, cloud, mobile and IoT.
  • Live examples. Real syntax and real tool usage in every chapter.
OSINT Exploitation Privilege escalation Evasion Incident response Threat hunting AI / ML Cloud IoT

Paperback and Kindle. For training, simulation and authorized environments only.

FREE RESOURCE - NO CERT NEEDED

The Complete
Hacker's Methodology
From Recon to Root

Every phase. Every technique. Real tools. Zero fluff.

Get the full methodology - free.

Drop your email and confirm it. The complete guide unlocks on its own page. No waiting. No PDF to download. Just the knowledge.

  • All 6 attack phases with real techniques and tools
  • 100+ offensive techniques mapped to MITRE ATT&CK
  • Key tools for each phase: Nmap, BloodHound, Mimikatz, and more
  • AD attack paths: Kerberoasting, DCSync, PetitPotam, Golden Tickets
  • Built from real grind - not recycled Medium posts

No spam. I share my notes, not your data.

CHECK YOUR INBOX

We sent a confirmation link to . Click it and the full methodology opens.

Don't see it? Check spam / promotions.

WHAT'S INSIDE
PHASE 01
RECONNAISSANCE
OSINTGoogle DorksGitHub DorksSubdomain EnumPort Scanning████████████████████
PHASE 02
ENUMERATION
FTP(21)SSH(22)SMB(445)MSSQLAD Enum█████████████████████
PHASE 03
EXPLOITATION
SQLiXSSLFI/RFISSTI█████████████████████████
PHASE 04
POST-EXPLOITATION
SUID/GUIDSudo Abuse█████████████████████████
PHASE 05
LATERAL MOVEMENT
Pass-the-Hash█████████████████████████
PHASE 06
PERSISTENCE
█████████████████████████████████
hacking_tees

Hacking Tees

Fifty-odd terminal-inspired tees for red teamers, devs, sysadmins and anyone who lives in a shell and would rather wear it too.

Scroll the drop →
Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design
On hamcodes.com Shop the tees
hamcodes_gear

Hamcodes Gear

Hoodies, hats, sweatshirts and the rest, for coders, hackers and anyone who builds the thing rather than talking about it.

Scroll the gear →
Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear
On hamcodes.com Shop the gear
Party game · 6 to 12 players · Ages 13+ · Print and play

Hacker in the Shadows

The hidden-role party game where the attacker has a staff badge.

You've been in the meeting where someone says they'd definitely know if the company had been breached. Hacker in the Shadows is a party game about how long that actually takes.

Everyone gets a staff badge, face down. Most of you are ordinary employees. One or two of you are Threat Actors, and your badge looks exactly like everyone else's until someone turns it over. Every night the Threat Actors quietly compromise a colleague. Every morning the survivors hold a standup, argue about the evidence, and fire someone. Occasionally the right someone.
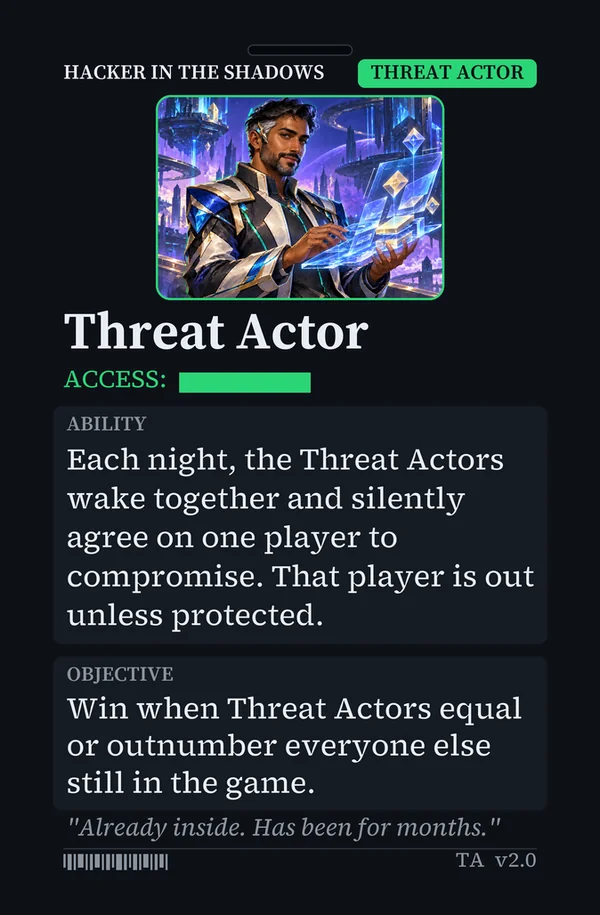
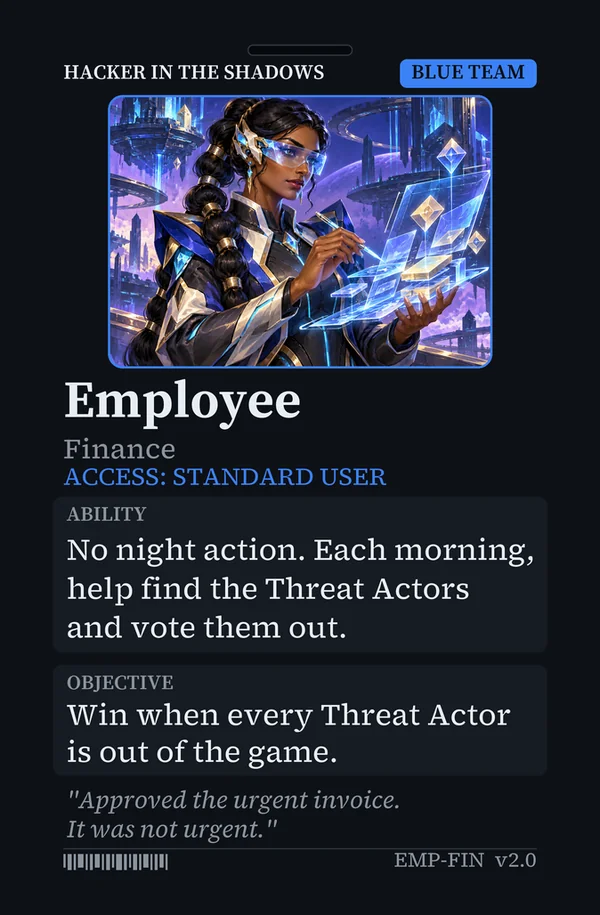
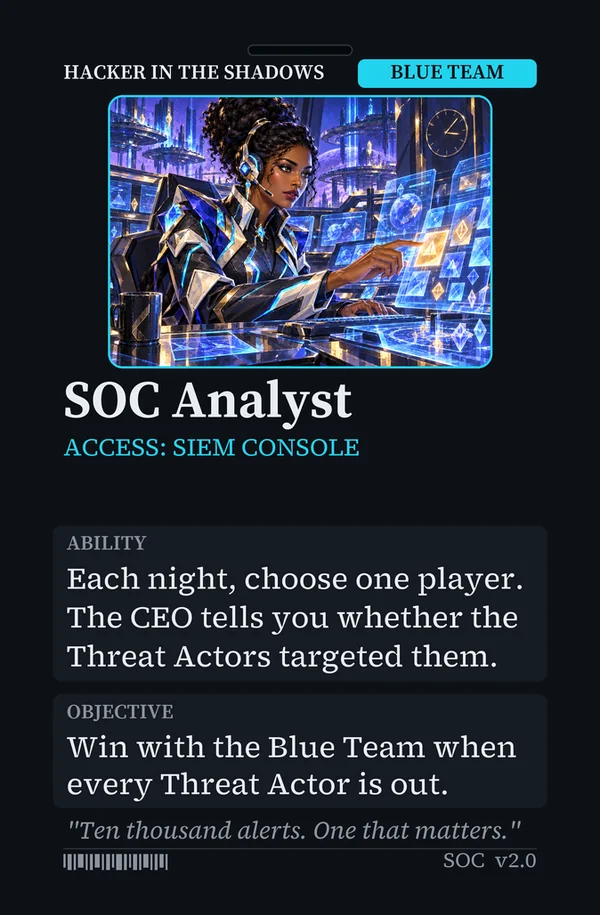
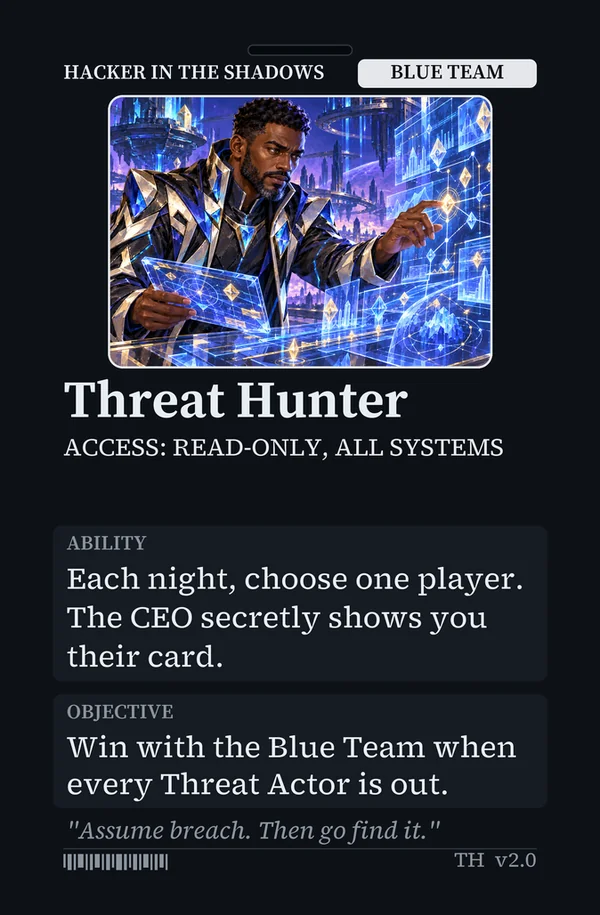
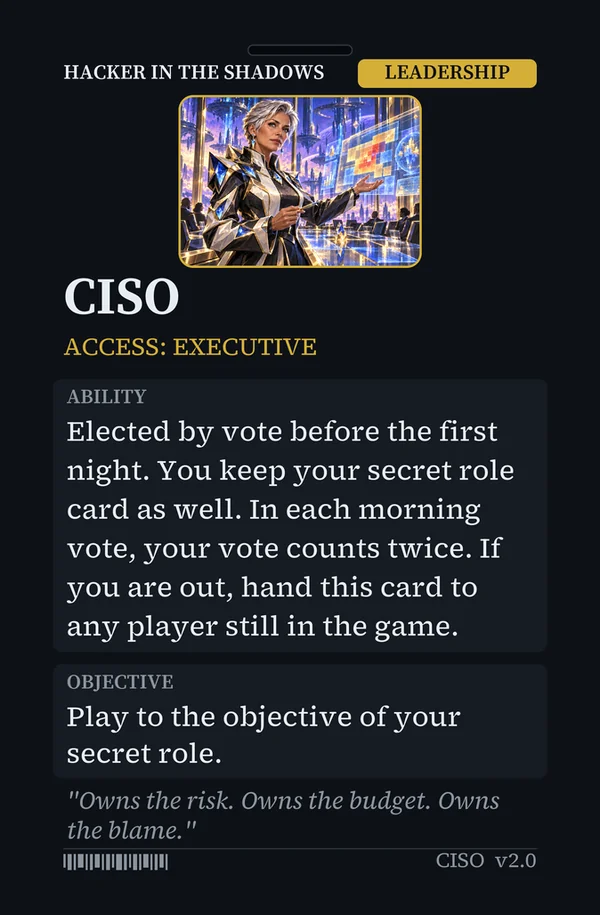
Hacker in the Shadows Threat Actor badge card, a smiling man in a white and blue jacket holding a glowing holographic display Hacker in the Shadows Employee badge card from the Finance department Hacker in the Shadows SOC Analyst badge card, an analyst watching a wall of dashboards Hacker in the Shadows Threat Hunter badge card, an analyst studying a timeline late at night Hacker in the Shadows CISO badge card, an executive presenting a risk heat map The back of a Hacker in the Shadows card, styled like a staff ID badge
01Night ShiftEveryone closes their eyes. The Threat Actors pick a target. The Threat Hunter checks a badge, the Security Engineer protects someone, and the SOC Analyst watches to see who gets hit.
02Morning StandupThe CEO reads out what happened overnight. Everyone argues. The CISO votes twice, because of course they do. Then the majority fires one suspect, and that badge gets turned over.
03Who winsThe Threat Actors win when they equal or outnumber everyone else. The Blue Team wins when every Threat Actor is out.

What's in the download: 53 cards on print-ready A4 sheets with crop marks, individual card files at 57 × 87 mm for a print shop, the rules on one page, and six reference cards.

  • Personal, $9. Print as many copies as you like for yourself, your family and your friends.
  • Team & Classroom, $29. Print as many copies as you need inside one organisation: one company, one school or one club. Built for security awareness days, team socials and lessons.

Get it on Gumroad Try the free Starter Shift

Want to test it on the team first? The free Starter Shift is eight cards on one A4 sheet, built for exactly six players and a moderator. Enough for a lunch break.

Played the original? The hats have been retired. Black Hat is now the Threat Actor, Blue Hat is the Employee, White Hat is the Threat Hunter, Red Hat is the Red Team Operator and the CTO is now the CISO.

If you play Magic: The Gathering, there's a free fan-made Commander deck with the same red team and blue team idea: PURPLE TEAM: Breach & Defend.

Free · Fan-made · For Magic: The Gathering players · Ages 13+

PURPLE TEAM: Breach & Defend

Red team finds it. Blue team fixes it. Purple team is where the two actually talk to each other.

This is a free Commander deck for people who already play Magic: The Gathering, built around exactly that loop. Kestrel Vane, the Red Team Lead, turns every successful attack into a Clue: a finding in the report. Ilse Varga, the Blue Team Lead, cracks those Clues and patches whoever survived. Red finds it, Blue fixes it, and the same creatures come back next turn. Which is, if we're honest, most of a security programme.
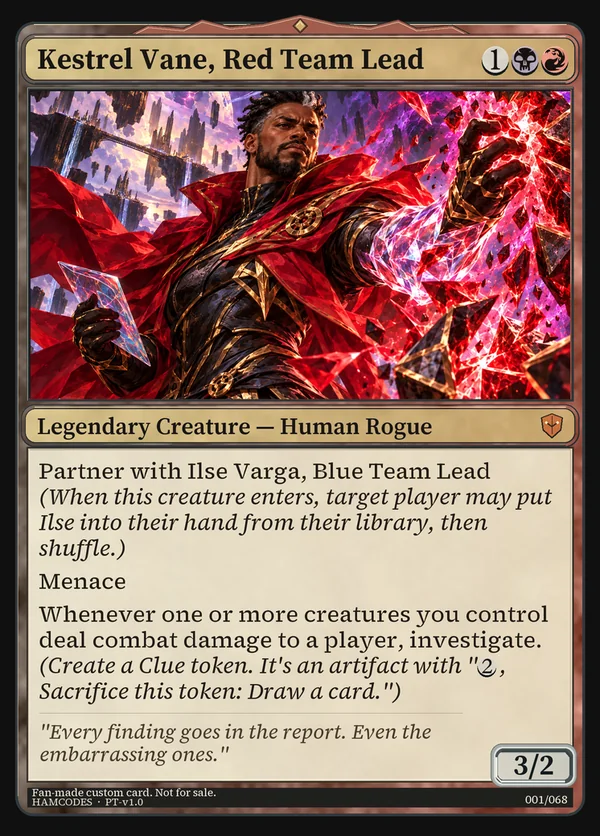
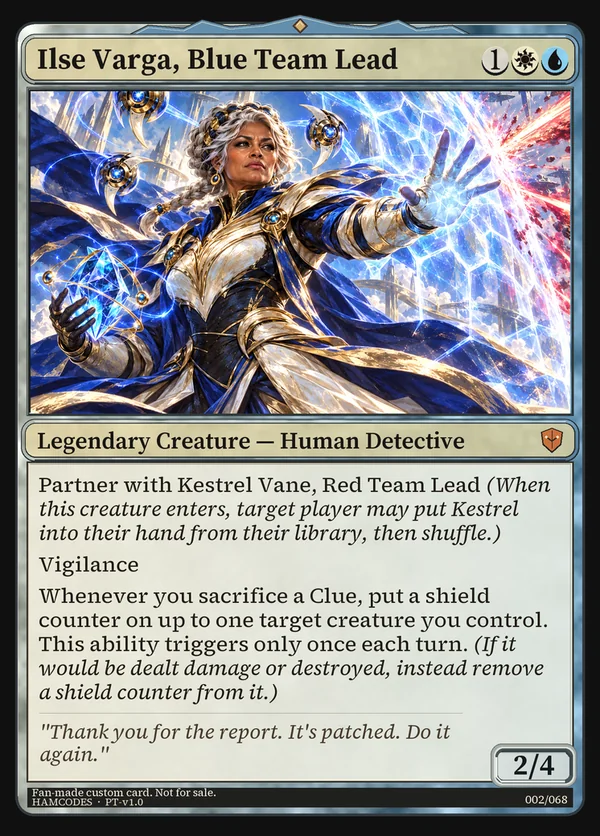
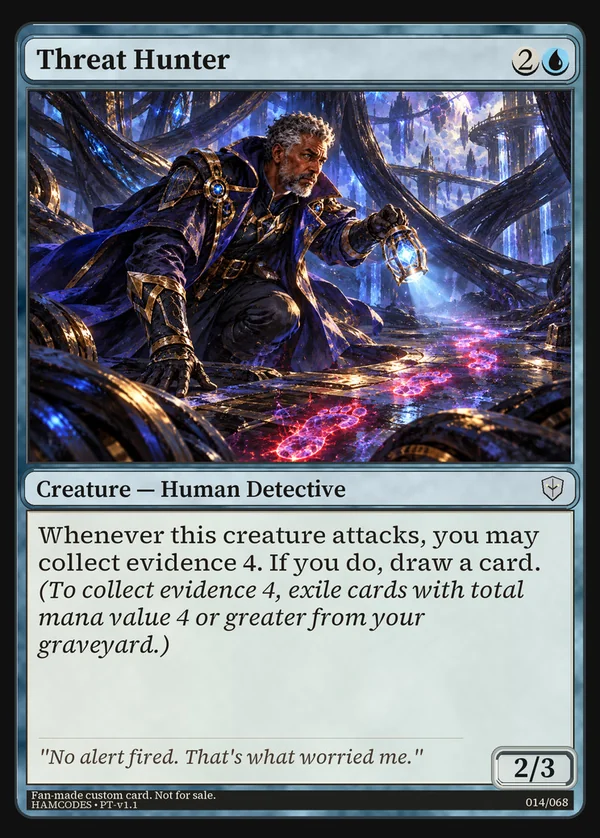
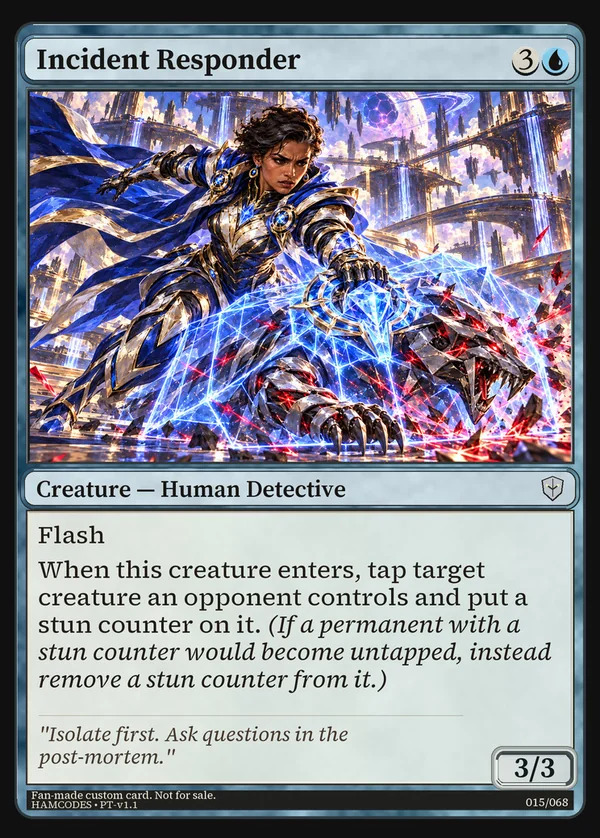
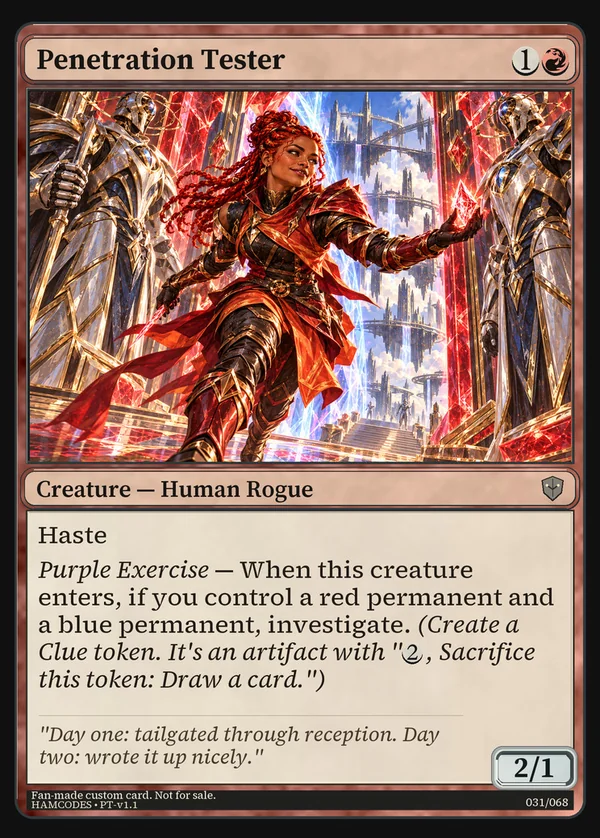
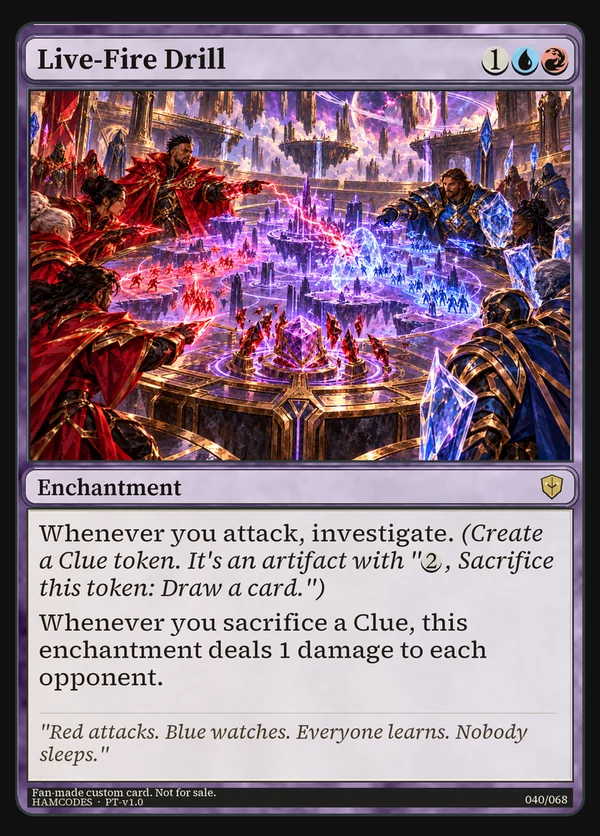
PURPLE TEAM card: Kestrel Vane, Red Team Lead PURPLE TEAM card: Ilse Varga, Blue Team Lead PURPLE TEAM card: Threat Hunter, a detective with a lantern following glowing red footprints PURPLE TEAM card: Incident Responder, a blue-armoured detective holding a shield of light around a mechanical beast PURPLE TEAM card: Penetration Tester, a red-haired rogue slipping between two armoured guards PURPLE TEAM card: Live-Fire Drill, red and blue teams around one table PURPLE TEAM card: Zero-Day Exploit, a red line of code slipping through a shield The back of a PURPLE TEAM card, a red and blue shield on a dark circuit pattern

What's inside: 100 cards ready to print, two partner commanders and every land included, plus 18 tokens. Every card is original, so there's nothing to buy.

Built for casual tables: lunch breaks, team socials, after-work games. Show the deck list before the first game and let the table veto anything that looks off.

Download the deck (PDF)

PURPLE TEAM: Breach & Defend is unofficial Fan Content permitted under the Fan Content Policy. Not approved/endorsed by Wizards. Portions of the materials used are property of Wizards of the Coast. ©Wizards of the Coast LLC.

Free to print, play and share. Not for sale.

Who this is for

Whichever side of the wire you are on

Red teamOffensive operators
Blue teamDefenders and threat hunters
Penetration testersExploitation and escalation
SOC analystsDetection and response
StudentsLearning it by doing it
Ethical hackersInfoSec on your own time